

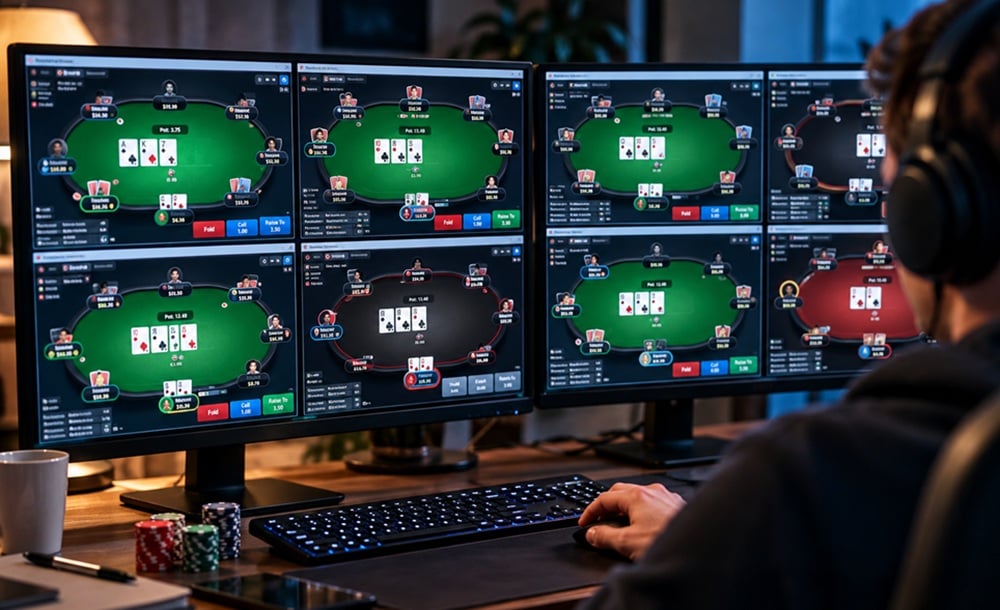
Based on reporting by Casino.org →
A sophisticated cheating scheme targeting online poker players has exposed significant vulnerabilities in the industry's security infrastructure. According to reporting from WIRED, attackers compromised Jurojin and IntuitiveTables, two software applications widely used by professional players who multi-table across platforms. By installing MeshAgent, a remote-access tool, the attacker gained the ability to view and control infected computers, effectively allowing real-time access to opponents' hole cards without breaching poker sites' security systems directly.
The scope of the breach appears substantial. While compromised software may have reached more than 1,000 users, investigators determined that malicious functions were activated selectively against high-stakes players, suggesting a targeted approach rather than indiscriminate fraud. One professional player, identified as Alex in WIRED's investigation, discovered MeshAgent after an AI assistant flagged the suspicious program in September. He documented 11 apparent screen-monitoring events while playing on Americas Cardroom, with the same suspicious opponent present during 10 of those sessions. Alex estimates his personal losses at approximately $30,000, though aggregate player losses are estimated at up to $4 million.
The industry response has been decidedly mixed, creating a troubling precedent for player protection standards. Americas Cardroom's operator, Winning Poker Network, conducted a review of more than two million hands involving accounts containing MeshAgent, including approximately 200,000 hands by the suspected cheater. The operator concluded it found no evidence of exploitation and declined to issue refunds. This decision has drawn criticism from affected players, particularly given the suspicious opponent's extraordinarily high win-rate and the documented screen-monitoring events.
Other platforms demonstrated contrasting approaches. CoinPoker banned a suspected cheating account and refunded over $100,000 to players, while ClubWPT Gold similarly banned an account and reimbursed affected customers. GGPoker responded more aggressively after receiving warnings from poker coach Patrick Howard about suspicious results. The platform introduced new detection measures for abnormally high win-rates, banned third-party poker software, traced suspected proceeds to a cryptocurrency wallet, and engaged law enforcement by requesting Coinbase preserve associated account records.
The fragmented response highlights a broader challenge facing the online poker industry: the absence of unified security standards and fraud investigation protocols. When operators reach contradictory conclusions about identical cheating methodologies and apply inconsistent player-protection measures, the industry's integrity suffers. Americas Cardroom's planned activation of ScreenShield protection by default on November 4, which will limit screen-capture and remote-viewing tools' ability to display cards, represents a step toward systemic improvement but comes too late for defrauded players.
This incident underscores a critical vulnerability in online poker's current architecture. The attack bypassed operator-controlled systems entirely by targeting third-party software, a vector many sites may not adequately monitor. As the industry continues to scale globally, with hundreds of operators managing millions of player accounts across dozens of jurisdictions, establishing baseline security requirements and standardized fraud-investigation protocols will become increasingly essential to player confidence and regulatory acceptance.
Source
Casino.orgRelated stories
Federal Court Seizes Victory Casino Cruises Vessel Over $791K Shipyard Debt
Canadian Player Battles 888 Over C$1.3M Jackpot Removal Following Software Malfunction
Utah Files 14 Criminal Charges Against Kalshi and Founders Over Sports Prediction Markets
Star Entertainment Ordered to Pay A$260M for Systemic AML/CTF Failures
More on CasinoAdvisor